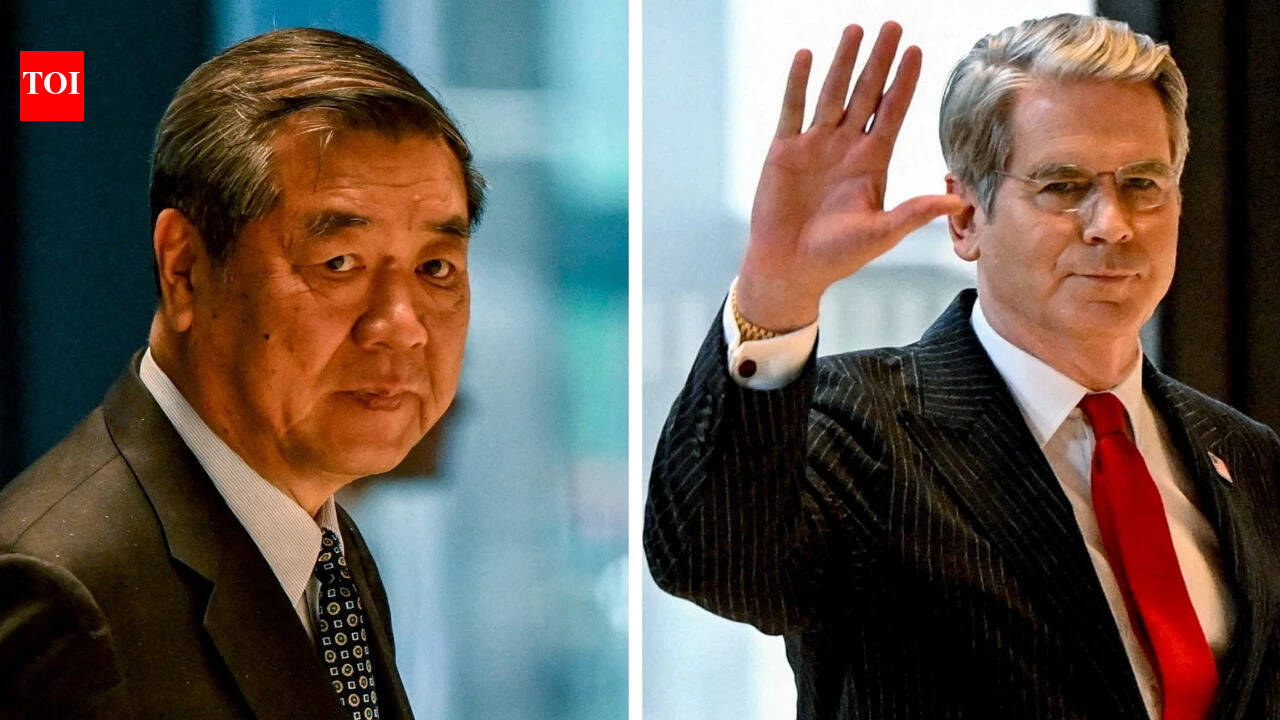
Harsh Jaiswal (left) and Rahul Maini. Three Indian-origin cybersecurity researchers, Harsh Jaiswal, Mohan Pedhapati and Rahul Maini, demonstrated how Anthropic's Claude AI could be used to exploit vulnerabilities and gain access to OpenAI employee accounts and the company's internal code repository, Wall Street Journal reported.The researchers, who work at cybersecurity startup Hacktron AI, carried out the research in July 2026 while investigating security weaknesses at leading AI companies. They eventually chained two separate vulnerabilities to move from OpenAI's public community forum to employee ChatGPT and Codex accounts and then to an internal GitHub repository.The researchers said the entire chain, from their initial discovery to demonstrating access to OpenAI's internal repository, took less than 72 hours. They spent under $3,000 on AI tokens and won a bounty of $6,500 after they disclosed the issues to OpenAI.How did the researchers get into OpenAI's systems?The attack began at community.openai.com, OpenAI's community and help forum, which is operated using the third-party platform Discourse.Hacktron researchers discovered that specially crafted HEIC/HEIF image files could...
Meet Harsh Jaiswal, Mohan Pedhapati and Rahul Maini: 3 Indian-origin researchers who used Claude to breach OpenAI systems, won $6,500 bounty
 2 days ago
21
Related


CNBC Daily Open: Everybody wants to rule the AI world
7 hours ago
7
Popular

El Niño rains in Peru disrupt access to Machu Picchu
1 month ago
291

 English (US) ·
© Clint's World News 2026. All rights are reserved
